
MCi Protects its Customers Worldwide with Enterprise-Grade Cyber Security
Serving state, local governments, and global Fortune 100 companies in the energy, mining, manufacturing, and chemicals industries, Management Controls, Inc. (MCi) needed to transform its cyber security to the world-class level expected by its long list of prestigious customers. As a software technology and services leader, MCi provides critical Software-as-a-Service (SaaS) solutions and its unique TRACK® platform for tracking and managing contract labor, equipment rental, and material spending. MCi counts many of the world’s largest companies as loyal customers, some of whom it has served for over twenty-five years.
Privately owned, the Houston-headquartered business has ambitions to grow in the U.S. healthcare, automotive, aerospace, chemical and upstream energy sectors and extend its footprint across North America, Europe, Asia, Australasia, and Africa. Safeguarding its customers’ data is essential to achieving its international expansion plans.
Customers demand world-class security
“Our customers are increasingly asking us detailed questions about our security, including disaster recovery and how we’ll respond to severe incidents. We must confidently reassure them that we have enterprise-grade protection in place,” explains Daniel Iturbe, Vice President of Infrastructure, Security & Compliance at MCi.
“To achieve this, we have implemented rigorous security protocols and business continuity and recovery plans that ensure the safety and confidentiality of our customer’s data. Our team of experts is continuously monitoring and updating these measures to stay ahead of potential threats.
“We understand that our customers trust us with their sensitive information, and we take that responsibility very seriously. Rest assured, our commitment to providing top-notch security measures is unwavering, and we are always ready to respond swiftly and effectively in any security incident.”
After completing a comprehensive program of preparation internally, MCi was ready to find a cyber security partner to provide a Security Operations Centre (SOC) that would match their business needs and meet the high standards of cyber security demanded by their customers worldwide.
MCi searched Quorum Cyber online, and a local Microsoft representative assured them they were worth talking to. Founded in 1989, MCi is predominantly in the cloud, and its cloud hosting is 100% provided by Azure. Hence, being a Microsoft-only house and a Microsoft Solutions Partner for Security, Quorum Cyber seemed like a good candidate. However, there were many other companies to assess as well.
Five essential criteria for a long-term partner
MCi took a diligent approach in selecting a long-term cyber security partner. They conducted an exhaustive Request for Proposal (RFP) discovery and execution phase over five months. During this time, they carefully evaluated over ten cyber security companies and thoroughly assessed their service offerings. Price was not the only determining factor, and the companies were assessed based on several essential criteria:
- Vendor qualifications: Experience, expertise, and financial stability.
- Technology and tools: A vital matrix component consisted of selecting a SOC company focusing only on Microsoft Azure Security Stack and Azure toolsets.
- Service Level Agreements (SLAs): Response times, escalation procedures, and reporting capabilities needed to comply with MCi contractual and compliance requirements.
- Flexibility and customization: The ability to tailor and customize services to meet MCi annual reports and audits for MCi customers.
- Security and compliance: SOC requirements to have Microsoft and industry-accepted certifications and accreditations.
- Cost and value: SOC’s pricing structure, schedule, add-on services, and overall were collectively categorized and analyzed independently.
- Reputation and references: The SOC’s reputation in the industry and references from current and past customers were scored using an internal MCi review process.
After evaluating all proposals, MCi trusted Quorum Cyber as their long-term cyber security partner. This decision was made after considering the added complexity of working with multiple vendors and that Quorum Cyber met all their requirements, including their need for an experienced and reputable Microsoft partner with a complete set of security competencies, certifications, advanced SIEM services, and strong customer support.
A true partner that lives and breathes cyber security
“I strongly believed that we needed a partner dedicated solely to the Microsoft ecosystem, who deeply understood cyber security and could fully support our Security Operation Center’s needs. We wanted a partner who would invest the time to comprehend our cloud infrastructure, unique business model, and even our customers and be part of our growth journey and continued success,” said Daniel.
Moreover, MCi needed an expert in Microsoft Sentinel, Azure, and cloud computing that can proactively detect and defend against zero-day attacks and possess strong automation skills to improve efficiency and reduce the risk associated with cyber incidents. The ideal partner should also have experience working within a single, integrated security ecosystem.
After onboarding MCi onto their SOC in early 2022, MCi is confident that Quorum Cyber, whose SOC team runs the Microsoft Sentinel Managed Detection & Response (MDR) service, has already helped to improve its cyber security posture and security scores significantly.
“I am thoroughly impressed by the exceptional customer service provided by Quorum Cyber. Their attention to detail, quick response time, and efficient triaging of information by their SOC is outstanding,” said Daniel.
“The single-pane-of-glass view offered by their customer portal, Clarity, has been an invaluable asset to my team. This enables us to access all the necessary information from one dashboard easily.
“Quorum Cyber’s technical expertise and account management skills are second to none, and their professionalism is truly commendable. They maintain continuous communication with their customers and offer top-notch customer support, a rare quality in today’s business world.
“Overall, Quorum Cyber is a fantastic extension of our organization and a true partner. Their unwavering commitment to excellence is reflected in every aspect of their services, making them a top-class provider in the cyber security industry.”
Peace of mind around the clock
“We couldn’t get the security and visibility of the SOC by recruiting more people to cover the same things in-house,” concludes Daniel. “In a nutshell, MCi has been able to catapult our cyber security posture to an enterprise-grade level, thanks to the mutual partnership in working towards the same goals.”

Partnership approach key to success at Renfrewshire Council
For Renfrewshire Council, situated in central, west Scotland, cyber security is about people and partnerships first and foremost. Technology simply provides the tools for people to collaborate to protect its assets and data, and minimise risk. How partners work together on all levels is crucial to strengthening the cyber security posture for the Council which, like all public sector bodies, needs to continuously defend itself against today’s threats and any that are just over the horizon.
Renfrewshire Council’s cyber security partnership with Quorum Cyber has grown from strength to strength since it began in 2019. Then, all Local Authorities in the UK needed to complete an annual Public Services Network (PSN) compliance health check, which consisted of vulnerability management and penetration testing among other assessments. Originally seeking professional support to pass their PSN health check, Quorum Cyber have since successfully tendered for more one-off engagements including advisory services.
Growing and learning together
Collaboration on projects has worked well, with both sides contributing and learning from each other along the journey and culminated in Renfrewshire Council partnering with Quorum Cyber when they tendered for a Security Operations Centre (SOC) team to monitor and protect their IT estate and multi-cloud environment around the clock. Quorum Cyber implemented the Microsoft Sentinel Managed Detection and Response (MDR) service in September 2022. The SOC team runs the MDR service 24 hours a day, 365 days a year to provide comprehensive protection and peace of mind.
From day one of the relationship, the Council was clear that it wasn’t interested in a simple transactional service; it wanted to extend its security team to exchange ideas and knowledge, develop its own services and grow together with a partner it could trust and call upon at any time should a cyber security incident occur. They were attracted by Quorum Cyber’s fresh, honest approach to cyber security.
“Price is never the driving factor when it comes to security partners,” says Carol Peters, Cyber Security Architect at Renfrewshire Council. “It was important for us to join up with a company that was going to be a true partner and we wanted an interactive one that could react fast when necessary.
“That partnership was essential for us and we’ve always had a very good relationship with Quorum Cyber. They are willing to help us deal with any incidents quickly, even if they are out of scope of the contract, or out of hours.”
Serving around 180,000 citizens in west, central Scotland, Renfrewshire Council needs to keep its physical and digital operations running for schools, medical centres, transport, businesses and the whole community, without interruption.
Cyber security is a business issue
The Council shares Quorum Cyber’s belief that cyber security isn’t really a technology issue, but a business issue where risk needs to be managed holistically. In the event of a sudden, damaging cyber-attack, systems and tools could be taken out of action at very short notice, or no notice – it’s then an urgent problem for the business.
“It’s important that cyber security is seen to be a business enabler and my cyber security strategy is aligned to the Council’s,” says Carol. “Quorum Cyber knows our architecture, they know us and our approach to cyber security.”
Protecting the whole community
As in any organisation, while building a strong cyber security posture is important, people are often the greatest asset, but only if they understand cybercrime. Employees need to be trained in how to spot phishing emails, maintain good cyber hygiene and stay safe online. One click on a malicious email could open the door to a breach which, in turn, could result in a ransomware attack later on.
This is why the Council is serious about cyber security education and training. The Council partnered with Get Safe Online, the UK’s leading internet safety organisation and in 2019, the Council launched Ren Safe Online to teach citizens and employees about threats on the internet. The Council was also the first in Scotland to launch the Get Safe Online Ambassador training programme, training volunteers about online safety and how to recognise when someone is at risk of harm due to online threats such as scams or bullying. Ultimately, the Council’s long-term partnership with Quorum Cyber is a joint operation about protecting families, children and essential community services, and people’s data, identities and finances.

Big Bus Tours finds the perfect cyber security partner
As the largest operator of open-top sightseeing bus tours in the world, Big Bus Tours helps over 5 million people explore some of the most famous cities on Earth every year. Tourists can hop on and hop off to visit the main highlights in cities across Europe, North America, the Middle East and Asia-Pacific.
Although it was successfully growing its business across four continents, the company acknowledged that it needed to overhaul its out-of-date and inadequate cyber security to protect its assets and its customer data. So when it was forced to freeze its services during the coronavirus pandemic, the IT team took the opportunity to simplify the whole security infrastructure, consolidating to a Microsoft security stack by June 2022.
Searching for the perfect partner
Part-way through the transformation programme they set out to find a qualified cyber security partner to protect their private equity-owned international business from the growing threats posed by cybercriminals to every organisation in any industry. They were specifically looking for a Security Operations Centre (SOC) to monitor and respond to any suspicious incidents across their IT estate around the clock.
Initially expecting this to be a fairly straightforward and easy exercise, they soon discovered they had to search high and low for a trusted Microsoft-first cyber security expert that could offer a simple, transparent service relevant to their needs. With a relatively small IT and security team, the company wanted to know exactly what security benefits and value they would receive for their investment.
However, despite a number of companies willing to work with them, it eventually took eight months for Big Bus Tours to identify the ideal UK-based partner that could deliver a service tailored to their needs and offer a fair price and sensible payment model to match. Quorum Cyber’s services and strong partnership approach was instantly very appealing.
Professional services with a simple, transparent pricing model
“It was the perfect fit,” says Dave Knowles, Chief Technology Officer for Big Bus Tours. “We found other companies to be very complicated to deal with – they just wouldn’t give us straight answers to our questions. Companies were trying to sell us things we didn’t need. It was a painful, frustrating experience and wasted a lot of our time.”
Before approaching Quorum Cyber, the tourism company’s cyber security set-up consisted of many different products and platforms from multiple vendors, making it laborious and time-consuming for the team to manage. Having started the transformation programme to consolidate their estate and move to a Microsoft-first environment, they needed a security partner who could support them on their journey and bring the right expertise to complement their own.
“One of the largest challenges we have is communicating with our diverse international team members – who aren’t all tech-savvy – to ensure they have adequate cyber security awareness training and don’t fall for the carefully crafted phishing emails we see,” explains Dave.
Feeling more confident after just the first conversation, Big Bus Tours signed up for the Microsoft Sentinel Managed Detection & Response (MDR) service. It’s run by Quorum Cyber’s SOC team who apply a combination of human ingenuity, knowledge and creativity backed by automated software to monitor an organisation’s entire IT estate.
Protection, confidence and peace of mind
“We feel that Quorum Cyber truly understands the ongoing threat landscape and protects our Chairman, C-suite and wider team from potentially dangerous phishing emails and other threats,” Dave continues. “Their team is very knowledgeable with their delivery, so we feel really confident in our security maturity and that we’re being looked after. I sleep much sounder knowing we have the Quorum Cyber team looking after us.”
Big Bus Tours’ short- to mid-term security goal is to maintain, or improve upon, the previous security score they were awarded in the parent company's security assessment. This is against a more unstable geopolitical climate during the past 12 months when cyber incidents have increased in frequency and complexity.
The company is looking forward to building on what the partnership has achieved so far. “The next step is for Quorum Cyber to help us be more proactive in our security operations and assist us in making the progress we’ve made just business as usual.”
Microsoft Solutions
- Microsoft Sentinel
- Microsoft Defender for Endpoint
- Microsoft Defender for Identity
- Microsoft Defender for Office 365
- Microsoft Defender for Cloud Apps
Leading housing association strengthens security to protect its tenants
As one of the leading housing associations in the UK and one of the largest in London and the south-east of England, Notting Hill Genesis (NHG) owns and manages 66,000 homes and employs around 2,000 staff. The organisation was created thanks to the merger in 2018 of Notting Hill Housing and Genesis Housing Association, two equally-sized associations with matching social values and purpose. With roots stretching back to the 1960s, NHG prides itself on caring for all of its tenants, its partnerships with the private sector and its vision for the future.
Unfortunately, housing providers haven’t been spared from the rise in cyber-attacks over the past few years and the UK has witnessed a number of damaging incidents. Although the sector might not seem like a priority target for cybercriminals, it can be seen as a relatively easy one that stores lots of people’s personal data. Associations that house thousands of tenants, and hold some of their private information, including addresses and bank details, have suffered from data theft. In some cases, threat actors obtained staff data too. While investigating these incidents, associations have sometimes needed to take their systems offline for an indefinite period of time, with the obvious consequence of disrupting the work of their employees or the quality and speed of services to their tenants.
Prevention is better than cure
In 2021, towards the end of a three-year deal with a major US technology company, NHG sought to replace its existing Security Operations Centre (SOC) with one that would be fit for their purpose and budget. They wanted a partner who could offer 24x7 monitoring, Incident Response capabilities and an expert on Microsoft Security technologies, which provided a continuous approach to cyber security. Microsoft referred the housing association to Quorum Cyber – a Microsoft Gold Partner and member of the Microsoft Intelligent Security Association (MISA) – and they made contact via our website.
In a climate where cyber threats were increasing exponentially, NHG were very familiar with the potential dangers. The management team knew that they needed an outsourcing arrangement which provided a Security Incident and Event Management (SIEM) platform to monitor all system-generated events and determine which ones could relate to a cyber-attack.
With a busy IT team already at full capacity, they wanted a service that provided cyber security experts to manage their response capability, from monitoring all the way through to incident response and containment. In the event of an attack, the Quorum Cyber SOC would manage and resolve the problem as soon as it was detected, working in close collaboration with NHG’s IT team.
Choosing the right cyber security partner
As part of their procurement process, NHG went out to tender for a managed security service. Ultimately, they chose a cyber security partner they trusted and felt confident could manage their end-to-end security operations but also provided a true sense of partnership and collaboration. This enabled them to focus on delivering high-quality housing services to their community in over 60,000 homes, ensuring that vital services for families and vulnerable individuals were never impacted.
On-boarding and risk mitigation
As housing associations and, indirectly, the tenants they have a duty of care of, are constantly at risk from data theft, time was of the essence. So, to protect NHG and their 200,000 customers, the organisation was swiftly on-boarded onto the SOC. During this step, a full Security Maturity Assessment (SMA) identified potential weaknesses and risk areas in their IT landscape. Furthermore, NHG completed an Incident Response Readiness Assessment to be fully prepared in the event of a breach in future.
Seamlessly expanding the security team
“Under Quorum Cyber’s protection, my team has the freedom to focus on our day jobs without worrying about the threat of an imminent attack,” says Richard Holland, Head of IT Systems and Cyber Security for NHG. “Thanks to a smooth and rapid on-boarding process, they were able to bolster our defences and empower us to rapidly resolve any incidents before they had a chance to damage our organisation.”
“Working with Quorum Cyber on a day-to-day basis has been a valuable experience,” explains Gavin Inns, NHG Security Manager. “It doesn’t feel like we’re hiring an external service provider but that we’ve extended our security team to beef up our defences. We’re confident we have the best skills, tools and personnel in place to defend Notting Hill Genesis from unknown threats.”

Containing A Major Global Security Incident
Just before the Christmas break of 2020, governments and organisations across the globe went into full emergency mode in an attack that has since then been labelled “Solorigate” (also referred to as SUNBURST by FireEye) – one of the biggest and most complex cyber-attacks of all time.
The cyber-attack, largely attributed to a Russian intelligence backed Threat Actor Group called Cozy Bear, employed tactics, techniques, and procedures (TTPs) that were of particular concern to national security.
The USA, believed to be their primary target, in what is being labelled an “unprecedented nation-state attack”, with very high-profile government entities affected such as the Commerce & Treasury department, Centre for Disease Control and the Justice Department.
Top cyber security experts speculate it may take organisations several months to fully understand the extent of the damage Solorigate has caused, including any data affected, identities compromised, or other high-value targets impacted.
The bad guys never sleep, so neither do we
As part of our 24x7 Security Operations Centre (SOC), the team at Quorum Cyber was paying very close attention when the news of Solorigate hit the headlines at around 03:00 am UK time.
While the world digested the news, we immediately began leveraging the power of the Microsoft security stack on their behalf. Our White Team (dedicated to the analysis of strategic threat intelligence) began threat hunting for the threat actor across our customers utilising the cutting-edge Microsoft Azure Sentinel (SIEM) and Microsoft 365 Defender (XDR) technologies.
The first stage was to triage customers who had been affected by the breach, to enable us to quickly quarantine compromised systems and execute Incident Response playbooks.
By isolating affected hosts and implementing enhanced monitoring across related assets, our team was able to have visibility across our customers – all within one hour of the public announcement of Solorigate.
By hour two, the team had issued affected customers a Major Incident Report, detailing exactly what this new threat was, the potential impact this could have had on their business operations, the actions Quorum Cyber undertook on their behalf and a complete breakdown of exactly what the next steps were to ensure full containment and remediation of the threat.
Protected before your first cup of coffee
Experts have speculated that Solorigate laid dormant in environments all over the globe since early Spring and has breached more than 18,000 organisations including the U.S Department of Homeland Security.
By harnessing the power of Azure Sentinel and Microsoft Defender, coupled with our own expert knowledge and skillsets, our team was able to detect, triage, and contain the threat to our customers before they had even learnt about the attack, or had their first morning coffee.
We help good people win
Solorigate provided Quorum Cyber with a unique opportunity to show our customers why we do what we do – we enable our customers to confidently operate in an increasingly hostile digital landscape, reducing risk and defending them against cyber security breaches and attacks.
This is for us what a SOC should be. And this is what is possible through our partnership with Microsoft. Our customers can rest assured, knowing the Quorum Cyber team will always unleash their passion, drive, and determination, combined with the best technology in the world, to keep their organisation safe.
"Recently, I saw the best of Quorum Cyber. While the world was learning about the Solorigate attack, our team started threat hunting across all our customers, harnessing the power of Azure Sentinel and Microsoft Defender.
As this incident has shown us all, cyber attacks and breaches can happen at any moment. For us, closing and submitting a Major Incident Report to our customers before they had even had their first cup of coffee is the absolute epitome of who we want to be, and one of the best ways to demonstrate value.
This is what is possible. This is Azure Sentinel. This is Quorum Cyber."
- Federico Charosky, Managing Director, Quorum Cyber
“In the face of a sophisticated cyber-attack, such as Solorigate, we are pleased to know that our mutual customers can rely on Quorum Cyber’s Azure Sentinel powered SOC & Microsoft Defender Managed Service to help protect their business, its people, and its customers.
We know that Quorum Cyber will continue to leverage the Microsoft security ecosystem – as well as making its own security expertise and risk mitigation strategies readily available – to help customers hunt, detect and remediate threats like Solorigate.”

Using Data to Identify Evolving Threats - Big Red Button - Phish
Big Red Button - Phish detected and protected legal clients from a new phishing attack that was targeting the legal sector in the UK.
This case is a perfect example of how machine learning and Big Data are key in our fight to keeping our customers, and their data, safe from cyber attacks.
Law firms are prime targets for the new breed of cyber criminals because they act as repositories for sensitive client data. In 2017 alone, Law firms across the UK lost a combined £85 million to cyber-attacks.
To find out more about 'Phish' our anti-phishing service, visit our website. Big Red Button – Phish is the only anti-phishing service that offers employee education, phishing simulation and phishing mitigation all in a single price per user package.

Cyber Security Strategy for the Oil & Gas Industry
The energy sector was shown to be the second most prone industry to cyber attacks in 2016 (Ponemon Institute), yet the industry’s cyber maturity remains stubbornly low. Learn how the Quorum Cyber team helped one company stand out from this trend, and implement a robust cyber security strategy to safeguard them well into the future.
The Client
Quorum Cyber partnered with our customer, an oil and gas company with offices worldwide, to design, build and deliver the first cyber security strategy for the organisation. By providing both the executive representation of cyber security to the senior management team, as well as operational BAU capabilities, Quorum Cyber was able to accelerate their IT transformation and adoption of cyber security best practices effectively and efficiently.
The Challenge
The customer has traditionally handled security as part of the tasks within the IT team. As the world changed and security became a bigger issue, the customer struggled to keep pace with the evolving landscape of threats. Ultimately this resulted in a risk exposure that was not understood, and that was only going to get worse unless immediate action was taken.
The objective for the customer was to improve their cyber security posture effectively and efficiently; however budget and internal governance constraints meant that it would take them too long to do that by themselves and would be prohibitively costly (as recruitment and retention of cyber security talent is a growing pain for most organisations).
The Solution: Security Director as a Service
Quorum Cyber’s Security Director as a Service is a perfect fit solution, where we provide an industry recognised expert to act on behalf of the customer as their security advisor to shape and deliver a maturity journey. This enables the customer to have access to a talent pool that would otherwise be too expensive to find and retain. Furthermore, the Security Director also has access to the rest of the Quorum Cyber family, that can help augment the delivery of security projects and BAU capabilities – such as a Security Operations Centre
The Results
The security director quickly established a cyber security strategy and improvement plan; built the business case for each initiative and drove them to successful completion. The security director provided executive-level visibility of the progress of the strategy, as well as operational level support to ensure the strategy was delivered as planned.
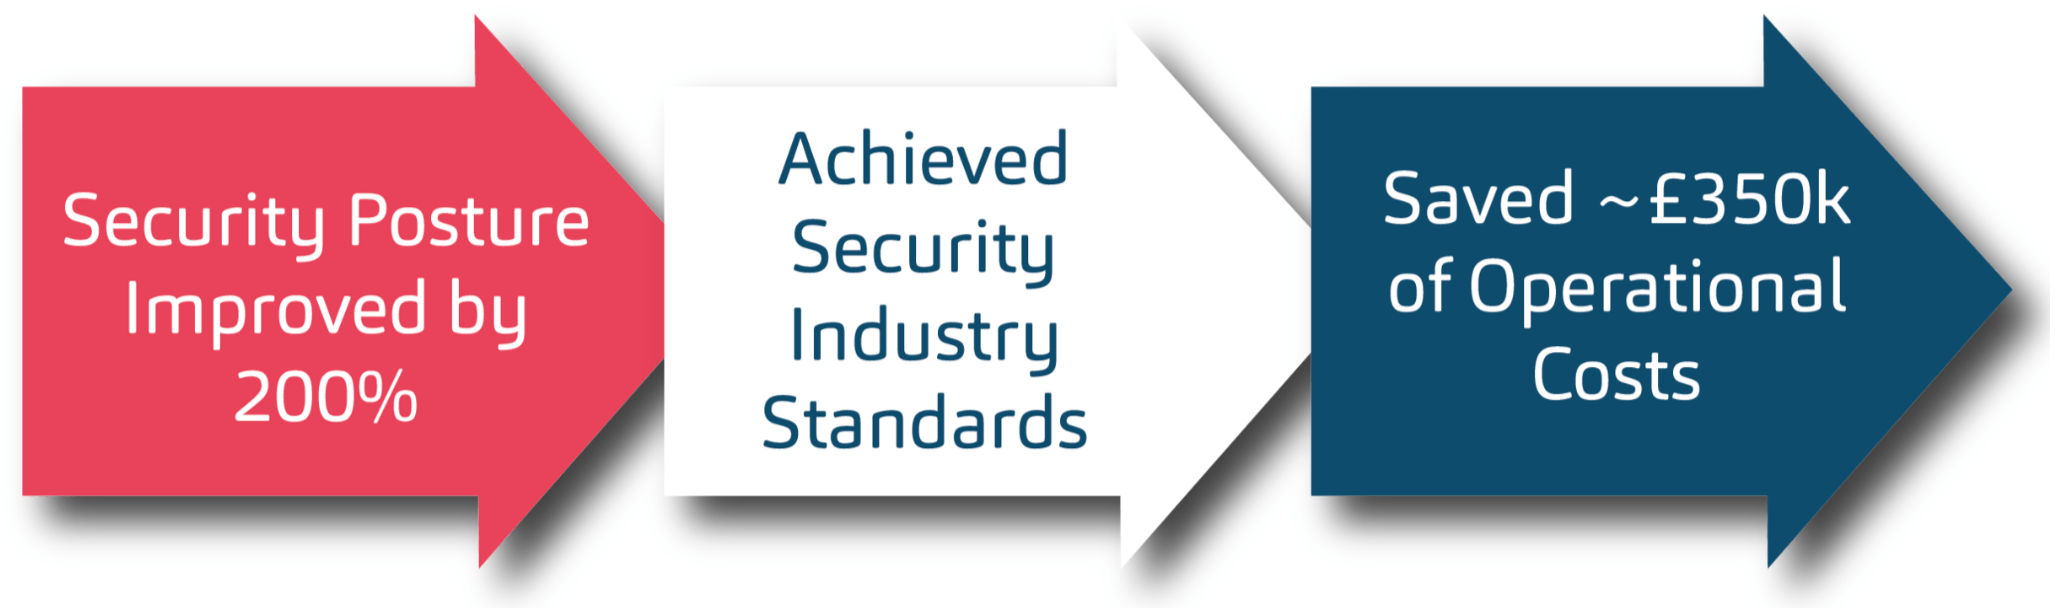
Within 12 months, we were able to improve the security posture of our customer by 200% as measured against accepted industry standards including the NCSC’s 10 Steps to Cyber Security and the NIS directive. Critical capabilities were deployed, including mature risk management frameworks, network security controls, increased user education, security incident detection and response, and modern malware protection capabilities.
By establishing a managed service capability to deliver these improvements, as opposed to having to do it through staff recruitment and retention, we were able to save the organisation approximately £350K of operational costs.
The customer continues to retain our services as Security Director and the relationship continues to grow, Quorum Cyber is now engaged in providing a series of managed services, including our Managed Defence and Managed Attack Subscriptions.
For further information on the support our Security Operations Centre and Professional Services teams can provide you and your organisation, contact the Quorum Cyber team today.
Azure Sentinel
Quorum Cyber helped a global employment, training and professional certification provider, establishing a leading Security Operation Center (SOC) capability, with Azure Sentinel at its core – increasing utilisation of their Microsoft licensing, and building an effective security strategy to achieve overarching business objectives.
The Client
A world-leading human services organisation, delivering employment, training and certification services and programs across 10 countries, throughout the key sectors of workforce development, health and wellbeing, community and corporate.
The Challenge
The organisation had limited capabilities for monitoring and responding to cyber security incidents, leaving them in a purely reactive position. Coupled with under-optimised tools and security systems, they were increasingly overwhelmed by a vast mix of true- and false-positive alerts, with only those of utmost severity recognised or responded to.
Given the increasingly urgent need to improve security, and the limitations of internal capabilities, outsourcing of detection and response to security incidents was identified as essential. They went to market to secure a SOC managed service, looking primarily at Splunk-based solutions.
The goal: to drastically reduce cyber risk through long-term improvement of their security posture.
The Results
As their security partners and Azure Sentinel SOC providers, we now deliver:
- 24/7 Monitoring of their entire estate;
- Optimisation of the organisation’s existing Microsoft investment and utilisation;
- Continuous attainment of the core business outcome driving the relationship: effective detection and response to security incidents.
While the client had originally sought out Splunk-based service providers, the Quorum Cyber team were able to convey the capability of Azure security solutions to not only match top competitors’ benefits like-for-like, but also their advantages:
- A 75% cost reduction over equivalent Splunk solutions;
- Increased utilisation of Microsoft tools already being paid for by the company;
- Greater efficiency and efficacy in incident detection and response.
Our Microsoft Azure expertise became the advantage, allowing us to directly address the business risk problem, and help the client get the best of each element of the Azure toolbox. All with our first-in-class, Azure Sentinel powered SOC services at the heart of the security operation.
Looking Forward
With the Quorum Cyber SOC solution, powered by Azure security solutions and lead by our team specialists, the client is successfully achieving their business objective: 24x7 incident detection and response, with increased trust that they will be well guarded against future cyber risks, attacks, or breaches.
What started as the provision of outsourced detection and response services for business units in 3 countries has grown into a long-term cyber security partnership, expanding services across all business units in the 10 countries within which they operate.

Azure Security Strategy
Quorum Cyber helped a global employment, training and certification provider in the swift response to an active incident, with recovery support leading to full adoption of the Microsoft security toolset. Quorum Cyber’s expert Azure engineering team achieved increased utilisation of their Microsoft licensing, to achieve their desired goals, displacing Splunk from client considerations.
The Client
A world leading human services organisation, delivering employment, training and certification services and programs across 10 countries, throughout the key sectors of workforce development, health and wellbeing, community and corporate.
The Challenge
Licensed for many Microsoft security tools, the client had done a small in-house installations, without expert support bringing knowledge or engineering specialism to the process. Left unattended, hundreds of alerts were un-responded to on their system, with no benefits realised from the product. The resultant customer perception was that the product offered little value.
During onboarding of the Azure Sentinel SOC by Quorum Cyber, we detected a cyber security breach in their finance department related to compromised accounts.
The challenge for Quorum Cyber was to provide incident response, before proceeding into processes of root cause identification, and putting in place the mitigating controls to prevent this breach from occurring again in future.
The Outcome
The customer engaged with Quorum Cyber to fix the Business problem of Cyber Security Risk exposure – they wanted to prevent, detect and respond to cyber security incidents. Not only did we deliver, but we exceeded expectations, with Microsoft technologies utilised in all areas of the client’s new security plans and
strategy:
- Azure Sentinel runs at the core of the Quorum Cyber SOC, displacing Splunk to provide continuous security improvements, at a significantly lower cost;
- MCAS is now being effectively rolled out and utilised, protecting the organisation from their most urgent threats – steering them away from other CASB solutions;
- Azure AD P2 and Defender ATP are now operational as additional mitigation controls, saving them from increased expenditures from going to market for alternatives.
The Quorum Cyber engineering and consulting teams are key in the continued improvements in utilisation and value capture of their existing investment. Working collaboratively to define: the strategy, the adoption of process, the implementation and consumption of the output, and improved perception of the Microsoft ecosystem.
This first success happened in their Australia Business Unit. The customer is now rolling out our Azure Sentinel SOC globally across their 9 other business units, bringing an increase in Azure adoption to:
- Seat count: 5000
- Node count: now at 250, with significant projected expansion.
Planning and continuous improvement processes across the client’s systems are also ongoing, repeating this experience with each vulnerability and corresponding Microsoft security product.
Lead by our Professional services team, we continue optimising utilisation of those tools already under license, with a roadmap for the global adoption of Azure Security Centre, Windows Defender ATP, Azure ATP, Azure AD P2, and Azure Information Protection now in place.
For further information on the support our Security Operations Centre and Professional Services teams can provide you and your organisation, contact the Quorum Cyber team today.

Big Red Button - Phish
Phishing is a cyber security attack that is low-risk, minimal cost, yet high potential reward for cyber criminals.
Like all law firms, our client was facing an ever increasing tide of phishing attacks on their email system. Despite having a traditional in-line scanning solution in place, many were still getting through, leaving the users with the illusion that they were safe.
Running a lean IT team meant that the firm’s resources were over stretched and the phishing attacks that were getting through (often the most dangerous ones) were not getting examined, leaving the firm at risk attacks such as credential theft, mail spoofing or trusted contact attacks.
To find out more about 'Phish' our anti-phishing service, visit our website. Big Red Button – Phish is the only anti-phishing service that offers employee education, phishing simulation and phishing mitigation all in a single price per user package.