Target Industry
Indiscriminate, opportunistic targeting.
Overview
A remote code execution (RCE) has been disclosed within SolarWinds Web Help Desk, tracked as CVE-2024-28986 (CVSS 9.8) that could allow attackers to run commands on the host machine. SolarWinds has released a hotfix that addressed the flaw, but authentication is required for successful exploitation.
Impact
Successful exploitation of CVE-2024-28986 would allow an attacker to run commands on the host machine.
Vulnerability Detection
A security patch has been released by SolarWinds with regards to the disclosed vulnerability. As such, previous product versions remain vulnerable to potential exploitation.
Affected Products
SolarWinds Web Help Desk (WHD) 12.8.3 and all previous versions.
Containment, Mitigations & Remediations
We strongly recommend that users of affected SolarWinds systems apply the SolarWinds Web Help Desk (WHD) 12.8.3 HF2 update as soon as possible.
Indicators of Compromise
No indicators of compromise (IoCs) are available currently.
Threat Landscape
SolarWinds occupies a significant portion of the IT management market share. The platform is used extensively within corporate networks across the industry sector spectrum. The Web Help Desk is widely utilised by large businesses, banks, and governments and is used to track and manage IT assets. Due to the wide adoption of this platform within many industries, successful exploitation of this vulnerability will likely have an impact on supply chains.
The Russian nation state-sponsored threat actor group, tracked as Midnight Blizzard, targeted SolarWinds in 2020 by deploying malicious code into the Orion IT monitoring and management software in a supply-chain compromise. Having been previously subjected to malicious cyber operations, it is therefore of critical importance to adhere to the recommended remediation and mitigation strategies to reduce the risk of exploitation.
Threat Group
No attribution to specific threat actors or groups has been identified at the time of writing.
Mitre Methodologies
CWE-502: Deserialization of Untrusted Data
Further Information
SolarWinds Trust Center Security Advisory
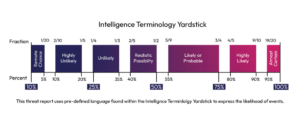
Intelligence Terminology Yardstick