Target Industry
Organisations across a broad range of industries are being actively targeted. Confirmed victims span retail, technology, aviation, finance, luxury goods, cloud service providers, and government contractors. The opportunistic nature of the attacks means any enterprise using Salesforce CRM or its ecosystem integrations could be at risk.
Overview
Throughout 2025, Salesforce instances and connected applications have become prime targets for data-theft campaigns. Threat actors are increasingly exploiting OAuth tokens, weak application governance, and social engineering (particularly vishing) to bypass authentication safeguards.
The most recent activity, attributed to UNC6395, involved the compromise of OAuth tokens linked to the Salesloft Drift app between 8–18 August 2025. Attackers systematically exported Salesforce data (including credentials, AWS keys, and Snowflake tokens) from multiple corporate environments. Salesloft has since revoked all Drift tokens, and Salesforce has removed the app from AppExchange pending investigation.
This campaign is part of a wider pattern of Salesforce-focused operations observed in 2025, with incidents affecting multiple high-profile organisations.
Impact
If successful, exploitation allows attackers to:
- Extract sensitive CRM data including customer records, cases, and user details.
- Harvest cloud credentials (AWS, Snowflake, VPN, SSO) for follow-on compromise.
- Conduct large-scale data theft leading to reputational harm, regulatory fines, and potential extortion.
- Enable persistent access to enterprise environments via OAuth abuse.
Vulnerability Detection
- Affected integrations include Salesforce instances connected to Salesloft Drift and other apps where OAuth scopes are overly permissive.
- Organisations should review Salesforce Event Monitoring logs, especially for unusual activity from Drift or other connected apps.
- Search CRM data for embedded secrets (e.g., AWS AKIA keys, Snowflake tokens, VPN URLs).
Exploitation
- UNC6395 actively exploited compromised OAuth tokens between 8–18 August 2025.
- ShinyHunters (UNC6040/UNC6240) and affiliates have been linked to widespread vishing and malicious app campaigns throughout mid-2025, distributing fake Salesforce Data Loader tools to obtain OAuth access.
Containment, Mitigations & Remediations
- Revoke & Rotate: Immediately revoke OAuth tokens for Drift or suspicious connected apps. Rotate exposed credentials and reset user passwords.
- Tighten App Governance: Restrict OAuth scopes to least privilege. Remove unused connected apps and enforce IP restrictions.
- Harden User Profiles: Define trusted login IP ranges and remove unnecessary “API Enabled” permissions.
- Enhance Monitoring: Enable Salesforce Shield or equivalent logging; review SOQL query activity for anomalies.
- Awareness & Training: Educate staff on vishing/social engineering risks, especially regarding OAuth authorisation requests.
Threat Landscape
Salesforce and its ecosystem integrations remain a lucrative target due to the volume of sensitive customer and business data they hold. Attackers are shifting away from exploiting platform vulnerabilities toward OAuth abuse and social engineering, highlighting the need for stricter app governance and employee vigilance.
These campaigns form part of a broader trend in which financially motivated groups like ShinyHunters leverage extortion and stolen data monetisation, while advanced actors experiment with supply-chain and app-ecosystem compromises.
Threat Group
- UNC6395: Identified in August 2025 Salesloft Drift exploitation. Focus on credential harvesting and cloud compromise.
- ShinyHunters / UNC6040 / UNC6240: Responsible for major vishing campaigns and fake Salesforce app distribution.
Further Information
https://cloud.google.com/blog/topics/threat-intelligence/voice-phishing-data-extortion
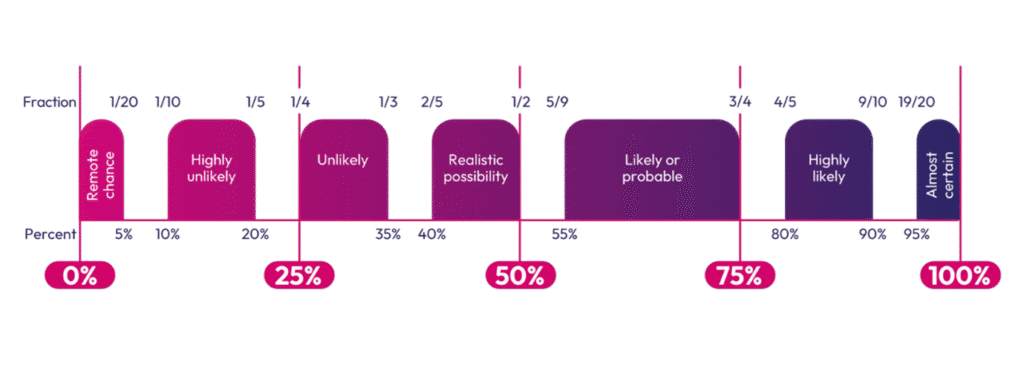
Intelligence Terminology Yardstick