Target Industry
Indiscriminate, opportunistic targeting.
Overview
Progress MOVEit is a secure managed file transfer software that is widely used and has previously been the subject of attacks by ransomware groups. A severe security flaw, tracked as CVE-2024-5806 (CVSS 3.1 base score: 7.4), has been discovered that requires the following conditions to be met:
- Acquisition of prior information such as a valid username
- The target account must be able to authenticate remotely
- The Secure File Transfer Protocol (SFTP) service must be accessible.
If these criteria are met, attackers can upload a public key to the server, sending the file path to the public key on the server instead of a valid public key, then sign the authentication request with the uploaded key.
Impact
Successful exploitation of CVE-2024-5806 could allow attackers to bypass authentication and carry out actions as the impersonated user, including access, modification or deletion of sensitive files.
Target Organisations
As of the time of writing, no specific organisations have been mentioned. However, the Shadowserver Foundation, a not-for-profit cybersecurity organisation has posted about seeing instances of the exploitation attempts.
Affected Products
MOVEit Transfer versions 2023.0.0 before 2023.0.11, 2023.1.0 before 2023.1.6 and 2024.0.0 before 2024.0.2.
Containment, Mitigations & Remediations
It is strongly recommended that organisations upgrade to 2023.0.11, 2023.1.6 and 2024.0.2 as a matter of urgency.
Indicators of Compromise
The ‘SftpServer.log’ will log failures to access the certificate store and may indicate a breach, in addition to empty string “” characters being displayed within the logs for validating the client key fingerprint.
Threat Landscape
Progress MOVEit occupies a significant portion of file transfer utilisation. Given that threat actors generally utilise a combination of probability and asset value to determine which attack surfaces to focus on, Progress MOVEit is a prime target. Due to the fact that Progress MOVEit has become an integral aspect of business operations, threat actors will continue to exploit vulnerabilities contained within the associated products in an attempt to extract the sensitive data contained therein.
Threat Group
No attribution to specific threat actors or groups has been identified at the time of writing.
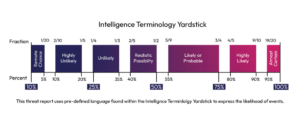
Intelligence Terminology Yardstick