Target Industry
Indiscriminate, opportunistic targeting.
Overview
A new OpenSSH unauthenticated remote code execution (RCE) flaw, named ‘regreSSHion’ has been discovered that provides root privileges on glibc-based Linux systems. OpenSSH is a suite of networking utilities based on the Secure Shell (SSH) protocol, which is used for a range of remote services as well as file transfers via Secure Copy Protocol (SCP) and Secure File Transfer Protocol (SFTP).
The flaw, tracked as CVE-2024-6387 (CVSSv3.1 score: 8.1), was discovered by Qualys back in May and is caused by a signal handler race condition in sshd that allows unauthenticated remote threat actors to execute arbitrary code as root.
Impact
Successful exploitation of CVE-2024-6387 could lead to full system compromise where a threat actor could execute arbitrary code with the highest-level privileges. This would likely result in a complete hijacking of the target system with potential follow up operations including malware deployment, data manipulation, and the creation of backdoors for persistent access.
Affected Products
The regreSSHion flaw impacts OpenSSH servers on Linux from version 8.5p1 up to, but not including, 9.8p1. Versions 4.4p1 up to, but not including, 8.5p1 are not vulnerable, resulting from a patch for CVE-2006-5051.
Versions older than 4.4p1 are vulnerable to regreSSHion unless they are patched for CVE-2006-5051 and CVE-2008-4109.
Qualys also highlighted that OpenBSD systems are not impacted by CVE-2006-5051 thanks to a secure mechanism introduced back in 2001. The researchers also noted that while the flaw likely also impacts macOS and Windows, its exploitability on these systems has yet to be verified.
Containment, Mitigations & Remediations
Qualys strongly recommends that the following mitigation steps are applied:
- Apply the latest available update for the OpenSSH server (version 9.8p1)
- Restrict SSH access using network-based controls such as firewalls
- Implement network segmentation to prevent lateral movement
- If the OpenSSH server cannot be immediately updated, users should set the ‘LoginGraceTime’ to 0 in the sshd configuration file but note that this can expose the server to denial-of-service (DoS) attacks.
Indicators of Compromise
No specific Indicators of Compromise (IoCs) are available currently.
Threat Landscape
OpenSSH occupies a significant proportion of the secure shell market share. Given that threat actors generally utilise a combination of probability and asset value to determine which attack surfaces to focus on, OpenSSH vulnerabilities will likely become a prime target. Due to the fact that OpenSSH is a commonly relied upon networking utility which is used for a range of remote services as well as file transfers via SCP and SFTP, threat actors will continue to exploit OpenSSH vulnerabilities in order to complete pre-defined objectives.
Threat Group
No attribution to specific threat actors or groups has been identified at the time of writing.
Mitre Methodologies
Common Weakness Enumeration (CWE)
CWE-364 – Signal Handler Race Condition
Further Information
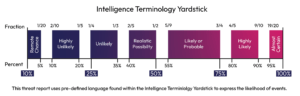
Intelligence Terminology Yardstick