Target Industry
Indiscriminate, opportunistic targeting.
Overview
Microsoft July 2024 Patch Tuesday: One hundred and forty-two vulnerabilities were addressed by Microsoft, two of which have been confirmed to have been actively exploited in the wild. A summary of the highlighted vulnerabilities has been outlined below:
First up is a Windows Hyper-V zero-day elevation of privilege (EoP), tracked as CVE-2024-38080 (CVSSv3.1 score: 7.8). Successful exploitation provides threat actors with SYSTEM-level privileges, with only more recent editions of Windows being impacted (Windows 11 since version 21H2 and Windows Server 2022 – including Server Core).
Microsoft also remediated a Windows MSHTML Platform zero-day, tracked as CVE-2024-38112 (CVSSv3.1 score: 7.5), a spoofing vulnerability affecting Microsoft’s MSHTML browser engine which is already under active exploitation. User interaction is required for compromise with threat actor having to lure victims into interacting with a malicious file.
A remote code execution (RCE) SharePoint vulnerability CVE-2024-38023 (CVSSv3.1 score: 7.2) was also included that could allow an authenticated threat actor with site owner permissions or higher to upload a specially crafted file to a SharePoint Server. Upon subsequently crafting malicious API requests to trigger deserialization of the file’s parameters, this enables threat actors to achieve RCE on the SharePoint Server.
Microsoft also disclosed that all supported versions of Windows are vulnerable to CVE-2024-38060 (CVSSv3.1 score: 8.8), a security issue in the Windows Imaging Component related to TIFF (Tagged Image File Format) image processing that could allow threat actors to execute arbitrary code on a system.
The final highlight of the 2024 Patch Tuesday release is the discovery of three critical CVEs related to the Windows Remote Desktop Licensing Service. Tracked as CVE-2024-38074, CVE-2024-38076, and CVE-2024-38077, all three have been assigned a CVSS 3.1 severity score of 9.8, meaning that if organisations rely on the Remote Desktop licensing service, patching should be an urgent priority.
Impact
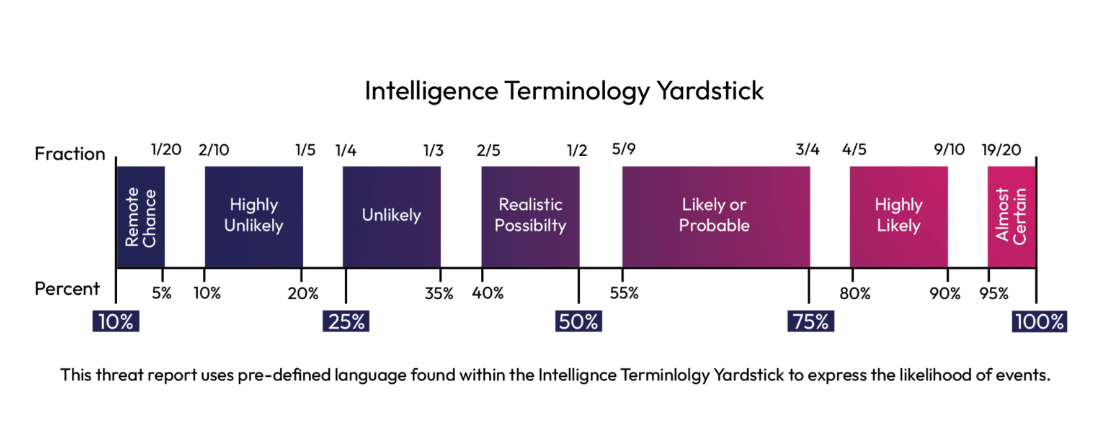
We have assessed that successful exploitation of the vulnerabilities outlined within the July 2024 Microsoft Patch Tuesday disclosure will likely result in the total loss of confidentiality, integrity, and availability of data within target systems.
Vulnerability Detection
Security patches for the vulnerabilities reported on have been released by Microsoft. Previous product versions therefore remain vulnerable to potential exploitation.
Affected Products
A full list of the affected products pertaining to the July 2024 Patch Tuesday can be found on the Microsoft July 2024 Security Update page.
Containment, Mitigations & Remediations
It is strongly recommended that the relevant security patches are applied to the respective Microsoft products as soon as possible. The patches can be found directly at the Microsoft Patch Tuesday July 2024 Security Guide.
Indicators of Compromise
No specific Indicators of Compromise (IoCs) are available currently.
Threat Landscape
Last month, Microsoft published remediations for 51 security flaws within the June 2024 Patch Tuesday release, including one zero-day and eighteen RCE flaws. Moving into the July disclosure, RCE and privilege escalation vulnerabilities continue to be leading attack vectors accounting for 41.5% and 18.3% of disclosed issues respectively, although security feature bypass vulnerabilities have surged to the same level, accounting for 16.9% of issues. Overall, the July 2024 Patch Tuesday disclosure resulted in the release of a significantly higher number of vulnerabilities this month, a stark contrast to the low number of flaw disclosure in recent months.
Threat Group
No attribution to specific threat actors or groups has been identified at the time of writing.
Mitre Methodologies
Tactics:
– TA0002 – Execution
– TA0004 – Privilege Escalation
Common Weakness Enumeration (CWE)
– CVE-2024-38080: CWE-190 – Integer Overflow or Wraparound
– CVE-2024-38112: CWE-668 – Exposure of Resource to Wrong Sphere
– CVE-2024-38023: CWE-502 – Deserialization of Untrusted Data
– CVE-2024-38060, CVE-2024-38077, CVE-2024-38076: CWE-122 – Heap-based Buffer Overflow
– CVE-2024-38074: CWE-191 – Integer Underflow (Wrap or Wraparound)
Further Information
Microsoft July 2024 Patch Tuesday Security Update
Intelligence Terminology Yardstick