Target Industry
Indiscriminate, opportunistic targeting, with a focus on users of technology companies and financial institutions.
Overview
A sophisticated cyber-attack campaign has emerged, targeting macOS users by exploiting GitHub Pages to distribute the Atomic Stealer (AMOS) malware. Threat actors are using Search Engine Optimisation (SEO) poisoning to elevate malicious repositories in search results, tricking users into downloading malware disguised as legitimate software installers from trusted companies such as LastPass, Dropbox, and others.
Impact
The cyber-attack leveraging GitHub Pages poses a serious threat to organisations, particularly those with remote or developer-heavy teams. By impersonating trusted brands and using SEO manipulation, threat actors trick users into downloading stealer malware capable of harvesting sensitive credentials and financial data. This not only risks internal system compromise but also damages brand reputation and may trigger regulatory consequences under data protection laws.
Exploitation
The attack begins when users search for legitimate software, such as “Install LastPass on MacBook,” and are unknowingly directed to malicious GitHub Pages through SEO-poisoned search results. These fraudulent pages then link to secondary staging sites that instruct users to execute a terminal command. This command initiates a CURL request to a base64-encoded URL, which resolves to a malicious shell script. Once executed, the script downloads the Atomic Stealer malware, cleverly disguised as a system update, thereby compromising the user’s macOS device.
Containment, Mitigations & Remediations
To mitigate the threat, users should avoid downloading software from unofficial sources and verify the authenticity of GitHub repositories before installation. Executing terminal commands from untrusted websites should be strictly avoided. Organisations are advised to deploy endpoint protection solutions capable of detecting macOS-specific threats.
Threat Landscape
This campaign reflects a growing trend of macOS-targeted malware and the abuse of developer platforms like GitHub. The use of SEO manipulation and social engineering tactics demonstrates a high level of operational sophistication. The threat actors have shown resilience, creating multiple GitHub usernames to bypass takedown efforts and maintain their infrastructure.
Threat Group
While the exact identity of the threat actors remains unconfirmed, the campaign is attributed to financially motivated cybercriminals. The use of Atomic Stealer, active since April 2023, suggests links to established malware distribution networks. The impersonation of high-profile brands and the scale of the operation indicate a well-resourced and organised group.
Tactics, Techniques and Procedures (TTPs)
- TA0001 – Initial Access: SEO poisoning, drive-by compromise
- TA0003 – Persistence: Installation of malware disguised as system update
- TA0006 – Credential Access: Theft of browser, system, and wallet credentials
- TA0011 – Command and Control: Exfiltration via remote servers
Indicators of Compromise (IoCs)
Domains:
- hxxps://ahoastock825[.]github[.]io/.github/lastpass
- hxxps://macprograms-pro[.]com/mac-git-2-download.html
- hxxps://bonoud[.]com/get3/install.sh
GitHub usernames:
- modhopmduck476
Further Information
Massive Cyber-Attack Attacking macOS Users via GitHub Pages to Deliver Stealer Malware
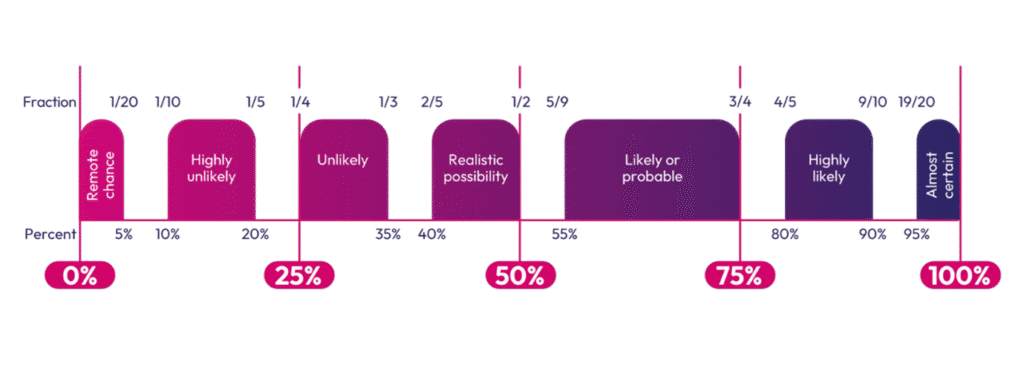
Intelligence Terminology Yardstick