Target Industry
FreePBX is an open-source private branch exchange (PBX) platform widely used by businesses, call centres, and service providers to manage voice communications.
Overview
Sangoma’s FreePBX Security Team disclosed a critical zero-day in the commercial Endpoint Manager module that enables unauthenticated access to the FreePBX Administrator, leading to arbitrary database manipulation (SQLi) and remote code execution (RCE) when the Administrator Control Panel (ACP) is exposed to the internet. The vulnerability assigned the CVE identifier CVE-2025-57819, carries a CVSS score of 10.0, indicating maximum severity. Threat actors began targeting multiple internet-connected FreePBX 16 and 17 systems on or before 21st August 2025.
Impact
Unauthorised access to FreePBX Administrator
- Attackers gain full control of the web UI, exposing SIP trunk credentials, extension secrets and call recordings. They can create/elevate accounts, change routing, and disable alerts to maintain stealth.
Arbitrary database manipulation
- Direct tampering with FreePBX/Asterisk tables enables inserting admin users, weakening ACLs, and rewriting routes to premium or attacker trunks. CDRs and audit trails can be altered or purged, hindering forensics and billing accuracy.
Unauthenticated remote code execution
- Code can be run as the PBX/web service account, allowing webshells, persistence (cron/systemd), and secret harvesting for lateral movement. Adversaries can deploy ransomware/crypto-miners or disrupt telephony services.
Full system compromise (potential)
- Chaining steps may yield root, letting attackers change firewall/SSH trust, implant durable backdoors, and repoint/brick phones via provisioning. This drives end-to-end loss of confidentiality, integrity, and availability – and rapid fraud exposure.
Affected Products
Endpoint module in:
- FreePBX 15 < 15.0.66
- FreePBX 16 < 16.0.89
- FreePBX 17 < 17.0.3.
Exploitation
- No public exploit code is currently available.
- Active exploitation of FreePBX in the wild with activity traced back as far as 21st August and backdoors being dropped post-compromise.
- Historical patterns suggest exploitation within days of PoC release, especially targeting internet-facing instances.
Containment, Mitigations & Remediations
- Apply vendor patches immediately for all affected versions:
- FreePBX 15: Upgrade to version 15.0.66
- FreePBX 16: Upgrade to version 16.0.89
- FreePBX 17: Upgrade to version 17.0.3.
- Restrict network access to FreePBX administration interface
- Implement strong network segmentation
- Use additional authentication mechanisms
- Monitor for any signs of unauthorised access or suspicious database activities
Threat Landscape
FreePBX underpins voice for many SMEs, call centres and MSPs, and its admin panel is often – sometimes inadvertently – reachable from the internet. CVE-2025-57819 (CVSS 10.0) collapses auth and input-validation boundaries in the commercial Endpoint module, enabling unauthenticated admin access, database tampering, and remote code execution (RCE).
Further Information
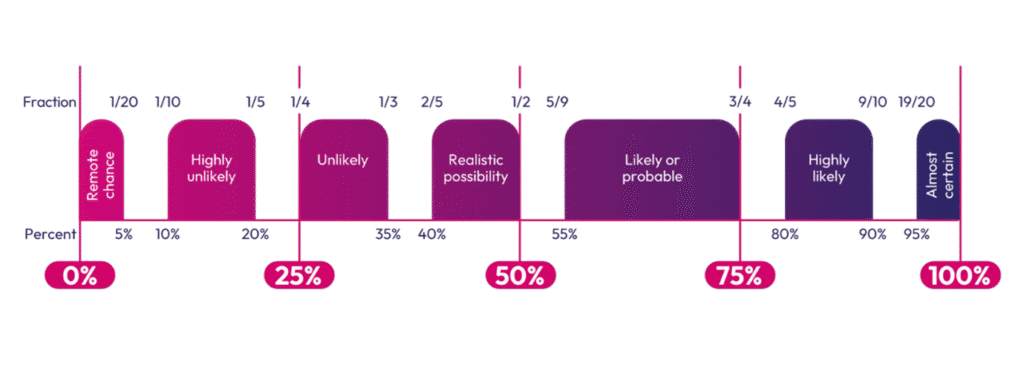
Intelligence Terminology Yardstick