Target Industry
Indiscriminate, opportunistic targeting.
Overview
A high-severity Docker vulnerability, tracked as CVE-2024-41110 (CVSS Score: 10.0), has been discovered. This vulnerability results in Docker Engines that use authorisation plugins for access control being open to authorisation bypass. Exploitation involves an attacker sending a specially crafted API request with a Content-Length of 0, thereby tricking the Docker daemon into forwarding it to the AuthZ plugin, which then cannot perform proper validation.
Impact
Successful exploitation of CVE-2024-41110 would likely allow threat actors to bypass authorisation plugins (AuthZ) under specific circumstances.
Vulnerability Detection
This vulnerability has been patched in Docker Engine versions v23.0.14 and v27.1.0. As such, previous versions are vulnerable to potential exploits.
Regardless of the version they operate, users who do not utilise plugins for authorisation, those who use Mirantis Container Runtime, and those who use Docker commercial products, are not affected by CVE-2024-41110.
Affected Products
For users who use authorisation plugins for access control, Docker Engine versions up to:
- 03.15
- 10.27
- 0.14
- 0.9
- 0.5
- 0.2
- 1.4
- 0.3
- 1.0
Containment, Mitigations & Remediations
It is highly recommended that all organisations update Docker Engine to versions v23.0.14 and v27.1.0 as soon as possible.
Users who cannot move to a safe version are advised to disable AuthZ plugins and limit access to the Docker API to trusted users only, following the principle of least privilege.
Indicators of Compromise
No indicators of compromise (IoCs) are available currently.
Threat Landscape
Docker holds a substantial portion of the containerisation market share. Considering that threat actors typically employ a blend of probability and asset value when identifying potential attack surfaces, container-based products like Docker could become a primary target. As Docker containers have become a crucial component of many business infrastructures, threat actors are likely to continue exploiting vulnerabilities in associated products in attempts to extract the sensitive data they contain.
Threat Group
No attribution to specific threat actors or groups has been identified at the time of writing.
Mitre Methodologies
Tactic
TA0004 – Privilege Escalation
Common Weakness Enumeration
- CWE-187 – Partial String Comparison
- CWE-863 – Incorrect Authorization
- CWE-444 – Inconsistent Interpretation of HTTP Requests (‘HTTP Request/Response Smuggling’)
Further Information
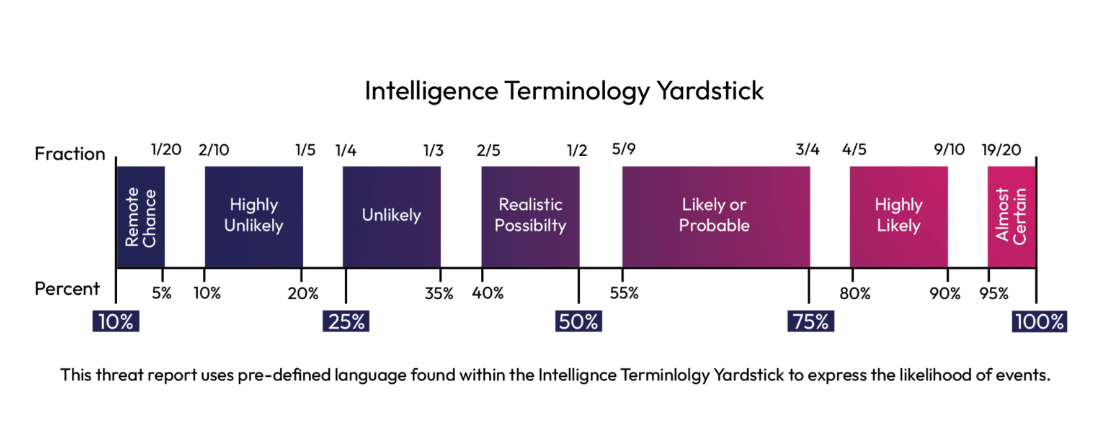
Intelligence Terminology Yardstick