Target Industry
Government agencies and cyber security organisations.
Overview
A set of vulnerabilities, collectively known as ReVault, has been found in Dell laptops used in sensitive environments like government agencies and cyber security firms. These vulnerabilities target the Broadcom BCM5820X security chip within Dell’s ControlVault3 firmware, which manages sensitive data like passwords and biometric information. The common vulnerability exposures (CVEs) which are used as part of the attack chain are:
- CVE-2025-25050 (CVSS 8.8) – Out-of-bounds write (code execution)
- CVE-2025-24922 (CVSS 8.7) – Stack-based buffer overflow
- CVE-2025-24919 (CVSS 8.6) – Unsafe deserialization in Windows APIs
- CVE-2025-25215 (CVSS 8.5) – Arbitrary memory free
- CVE-2025-24311 (CVSS 8.3) – Out-of-bounds read (info leakage)
Affected Products
- Latitude series
- Precision series
- Rugged series
- Pro Plus and Pro Max lines
Impact
These vulnerabilities can be exploited remotely or physically, threatening device integrity, user identity, and regulatory compliance. Organisations are likely to face operational disruptions, data breaches, and reputational damage if affected devices are not promptly patched.
Exploitation
The ReVault vulnerabilities are exploited through remote or physical access. Remotely, threat actors can use Windows APIs without admin rights to run malicious code in the firmware, gaining access to sensitive data and installing malware that survives system resets. Physically, attackers can tamper with the device’s security hardware to bypass biometric authentication and gain full system access.
Containment, Mitigations & Remediations
It is highly recommended to update the firmware to the latest version. Refer to DSA-2025-053 for detailed remediation guidance.
Threat Landscape
The ReVault vulnerabilities in Dell’s ControlVault3 firmware pose serious risks to organisations by allowing attackers to steal credentials and biometric data, install persistent malware that survives system resets, and bypass biometric authentication entirely.
Threat Group
The specific threat group behind this has not been publicly identified at the time of writing.
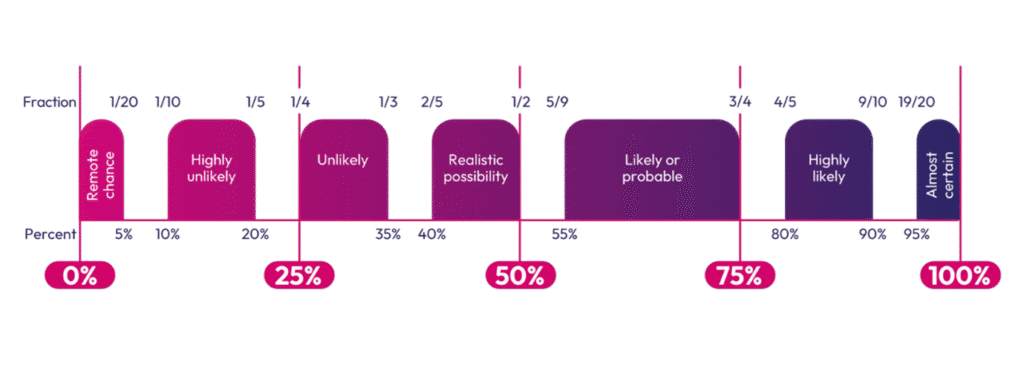
Intelligence Terminology Yardstick