Overview
Reports from around the world indicate that an update pushed out by the infosec vendor CrowdStrike is causing Windows machines to crash whilst displaying the Blue Screen of Death (BSoD) and then being unable to reboot. CrowdStrike is aware of the reports of crashes on Windows hosts related to Falcon Sensor, an agent that the infosec vendor claims “blocks attacks on your systems while capturing and recording activity as it happens to detect threats fast”.
Microsoft confirmed that it is taking “mitigation actions” whilst investigating issues with cloud services in the US, and an issue impacting several of its apps and services.
As of the time of this intelligence report, this issue has caused IT outages across the globe, currently affecting airlines, media and banks. CrowdStrike engineers are working on the issue, however, this is a rapidly developing situation, and the Quorum Cyber Threat Intelligence team will provide any updates as soon as possible.
Impact
This issue has caused global IT outages with several high-profile organisations being impacted.
Companies around the world have been unable to reboot, according to reports. In the UK, railway companies have reported delays whilst some GP surgeries in England are having issues with booking appointments. In the US, American Airlines says none of its flights are taking off. The issue has also extended to the media sector with Sky News not being able to broadcast live, according to its executive chairman.
Affected Products
Windows hosts with the CrowdStrike Falcon Sensor agent.
Containment, Mitigations & Remediations
As of 7:30am UTC on 19th July 2024, Brody Nisbet, CrowdStrike’s chief threat hunter, confirmed the issue and on X posted workarounds which have been outlined below:
- Boot Windows into Safe Mode or the Windows Recovery Environment
- Navigate to the C:\Windows\System32\drivers\CrowdStrike directory
- Locate the file matching “C-00000291*.sys” and delete it.
- Boot the host normally.
Threat Group
As of the time of this intelligence report, there is no indication that this issue has been caused by actions of a malicious cyber actor, but has rather resulted from a faulty csagent.sys file from the CrowdStrike update.
Further Information
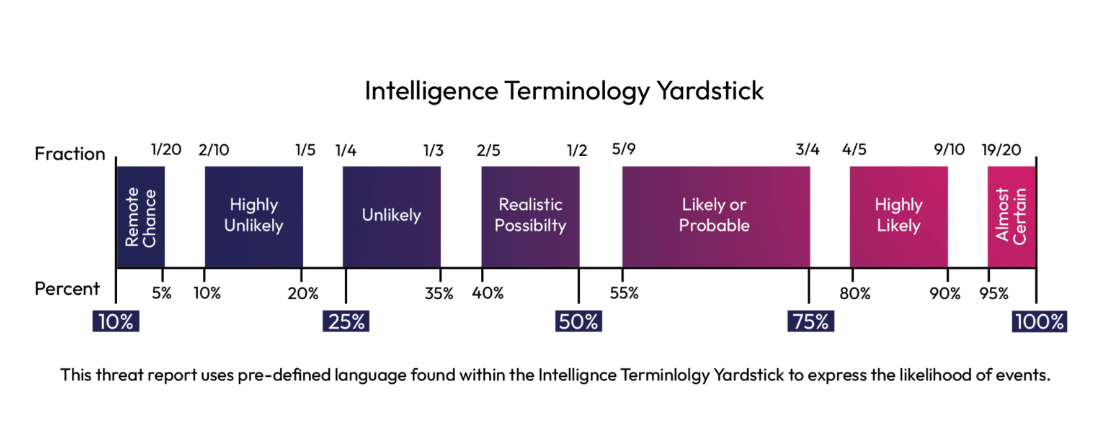
Intelligence Terminology Yardstick