Target Industry
Indiscriminate, opportunistic targeting.
Overview
PHP is an open-source scripting language utilised in web development across Windows and Linux servers. A severe security flaw has been discovered that arose from the encoding conversion of Unicode characters to ASCII in the Windows feature ‘Best Fit’ when PHP is used in CGI mode, which allows for unauthenticated attackers to execute arbitrary code through argument injections on remote systems. Tracked as CVE-2024-4577 (CVSS 3.1 base score: 9.8) the relevant security update should be applied as a matter of urgency where possible.
Impact
Successful exploitation of CVE-2024-4577 could allow attackers to conduct remote code execution (RCE).
Targeted Organisations
As of the time of writing, no specific organisations were targeted apart from PHP.
Affected Products
All versions of PHP installed on Windows operating system.
Containment, Mitigations & Remediations
It is strongly recommended that upgrading to versions 8.1.29, 8.2.20 and 8.3.8 are carried out as soon as possible.
Indicators of Compromise
No specific Indicators of Compromise (IoCs) are available currently.
Threat Landscape
PHP occupies a significant portion of server-side scripting language utilisation. Given that threat actors generally utilise a combination of probability and asset value to determine which attack surfaces to focus on, PHP is a prime target. Due to the fact that PHP has become an integral aspect of business operations, threat actors will continue to exploit vulnerabilities contained within the associated products in an attempt to extract the sensitive data contained therein.
Threat Group
No attribution to specific threat actors or groups has been identified at the time of writing.
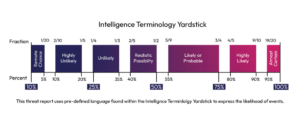
Intelligence Terminology Yardstick