Intelligence Cut-off Date (ICoD)
28/06/2024 at 12:00 UTC
Overview
The international technology company, TeamViewer, is investigating a possible intrusion of its internal corporate IT environment after discovering irregularities on 26th June. The company stated that the attack was linked to credentials of an employee account within its corporate IT environment, with incident response measures immediately enforced.
It also disclosed that there was no evidence to indicate that the product environment or customer data have been compromised, because TeamViewer’s internal corporate IT environment is completely independent from the product environment. However, the company, with the help of experts, has attributed the activity to the Russian state-sponsored threat actor, tracked as Midnight Blizzard.
Investigations are still ongoing and, as such, the Quorum Cyber Threat Intelligence team will provide updates as and when further details emerge.
Impact
Whilst there is currently no confirmation of a breach in TeamViewer product environments or of customer data, its widespread corporate usage means that any reported breach would almost certainly provide full access to internal networks.
Affected Products
TeamViewer Remote Access Software
Containment, Mitigations & Remediations
As of the time of this intelligence report the exact method of breach is unclear. However, there is nothing to indicate that this relates to a vulnerability in the TeamViewer application itself. Although there is not enough information available to provide effective recommendations, updating to the latest software version should not be discouraged.
Indicators of Compromise
No specific Indicators of Compromise (IoCs) for this incident are currently available. However, we will provide updates as further details emerge.
Threat Landscape
TeamViewer software allows users to remotely control systems. It is currently being used by over 640,000 clients worldwide and has been installed on over 2.5 billion devices since the organisation was founded. It should be noted that TeamViewer was also targeted by Chinese hackers back in 2016 and by unidentified actors accessing water sector SCADA controls in 2021.
Nation State Threat Actor Profile
TeamViewer issued a statement on 28th June attributing the incident to the Russian state actor group, tracked as Midnight Blizzard.
The Quorum Cyber Threat Intelligence team has previously assessed that Midnight Blizzard likely operates under the direction of the Russian Foreign Intelligence Service (SVR). The state actor employs a wide variety of advanced techniques in its cyber operations in support of the SVR’s intelligence collection requirements and dedicated espionage of foreign interests. Midnight Blizzard applies a wide range of bespoke tools developed in a variety of programming languages, whilst utilising a range of initial access methods that include stolen credentials, supply chain attacks and the deployment of the Active Directory Federation Services (ADFS) malware, named as FOGGYWEB and MAGICWEB.
Midnight Blizzard Targeting Profile
Midnight Blizzard primarily targets government, inter-governmental and non-governmental organisations (NGOs), as well as think tanks, military, IT service providers, health technology, research, and telecommunications entities based in or operating out of North Atlantic Treaty Organisation (NATO) states, including the US, the UK, and Western Europe.
Midnight Blizzard Toolset
Although no IoCs are currently available for this incident, the Quorum Cyber Threat Intelligence team has assessed with high confidence that the state actor leverages the following toolset within its tradecraft to conduct its offensive operations:
- PinchDuke: Toolkit that consists of multiple loaders and a core information stealer trojan
- CosmicDuke: Information stealer malware
- GeminiDuke: Toolset that consists of a core information stealer, a loader and multiple persistence-related components
- CozyDuke: Modular malware platform that can be instructed by a command-and-control (C2) server to download and execute arbitrary modules
- OnionDuke: Toolkit that includes at least a dropper, a loader, an information stealer trojan and multiple modular variants
- SeaDuke: Backdoor malware that focuses on executing commands retrieved from its C2 server, such as uploading and downloading files, executing system commands, and evaluating additional Python code
- POSHSPY: Backdoor that leverages PowerShell and Windows Management Instrumentation (WMI).
Further Information
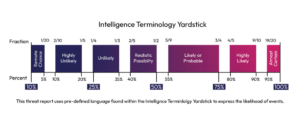
Intelligence Terminology Yardstick