Target Industry
Indiscriminate, opportunistic targeting.
Overview
Citrix has disclosed details relating to these vulnerabilities for NetScaler, Citrix Workspace app, Citrix Provisioning, Windows Virtual Delivery Agent for CVAD, and Citrix DaaS:
- [CVE-2024-5491] (CVSSv4 score 7.1): NetScaler ADC and NetScaler Gateway denial of service vulnerability.
- [CVE-2024-5492] (CVSSv4 score 5.1): NetScaler ADC and NetScaler Gateway open redirect vulnerability.
- [CVE-2024-6235] (CVSSv4 score 9.4): NetScaler Console access control vulnerability.
- [CVE-2024-6236] (CVSSv4 score 7.1): NetScaler Console, NetScaler Agent, and NetScaler SVM denial of service vulnerability.
- [CVE-2024-6148] (CVSSv4 score 5.3): Citrix Workspace app for HTML5 access control vulnerability.
- [CVE-2024-6149] (CVSSv4 score 4.8): Citrix Workspace app for HTML5 open redirect vulnerability.
- [CVE-2024-6286] (CVSSv4 score 8.5): Citrix Workspace app for Windows privilege escalation vulnerability.
- [CVE-2024-6150] (CVSSv4 score 4.8): Citrix Provisioning access control vulnerability.
- [CVE-2024-6151] (CVSSv4 score 8.5): Windows Virtual Delivery Agent privilege escalation vulnerability.
Impact
- Exploitation of CVE-2024-6236, CVE-2024-5491, or CVE-2024-6150 allows threat actors to disrupt the normal functioning of the target machine.
- Exploitation of CVE-2024-6151 or CVE-2024-6286 allows a local user to escalate privileges.
- Exploitation of CVE-2024-6235 can lead to sensitive information disclosure.
- Exploitation of CVE-2024-6148 allows threat actors to bypass GACS Policy Configuration settings, gaining unauthorized access to protected resources and carrying out actions they should not be able to perform.
- Exploitation of CVE-2024-5492 or CVE-2024-6149 allows threat actors to redirect users to a vulnerable URL.
Vulnerability Detection
Citrix has released patches pertaining to the security flaw for the respective product versions. As such, previous versions are vulnerable to the potential exploits.
Affected Products
NetScaler ADC and NetScaler Gateway (CVE-2024-5491, CVE-2024-5492):
- NetScaler ADC and NetScaler Gateway 1 before 14.1-25.53
- NetScaler ADC and NetScaler Gateway 1 before 13.1-53.17
- NetScaler ADC and NetScaler Gateway 0 before 13.0-92.31
- NetScaler ADC 13.1-FIPS before 13.1-37.183
- NetScaler ADC 12.1-FIPS before 12.1-55.304
- NetScaler ADC 12.1-NDcPP before 12.1-55.304
NetScaler Console (formerly NetScaler ADM) (CVE-2024-6235):
- NetScaler Console 14.1 before 1-25.53
NetScaler Console, NetScaler Agent and NetScaler SVM (CVE-2024-6236):
- NetScaler Console 14.1 before 1-25.53
- NetScaler Console 13.1 before 1-53.22
- NetScaler Console 13.0 before 0-92.31
- NetScaler SVM 14.1 before 14.1-25.53
- NetScaler SVM 13.1 before 13.1-53.17
- NetScaler SVM 13.0 before 13.0-92.31
- NetScaler Agent 14.1 before 1-25.53
- NetScaler Agent 13.1 before 1-53.22
- NetScaler Agent 13.0 before 0-92.31
Citrix Workspace app for HTML5 (CVE-2024-6148, CVE-2024-6149):
- Citrix Workspace app for HTML5 before 2404.1
Citrix Provisioning (CVE-2024-6150):
- Citrix Provisioning versions before 2402
- Citrix Provisioning versions before 2203 LTSR CU5
- Citrix Provisioning versions before 1912 LTSR CU9
Windows Virtual Delivery Agent:
- Citrix Virtual Apps and Desktops versions before 2402
- Citrix Virtual Apps and Desktops 1912 LTSR before CU9
- Citrix Virtual Apps and Desktops 2203 LTSR before CU5
Citrix Workspace app for Windows
- Citrix Workspace app for Windows versions before 2403.1
- Citrix Workspace app for Windows versions before 2402 LTSR
Containment, Mitigations & Remediations
It is highly recommended that all organisations apply the relevant patches as soon as possible.
Indicators of Compromise
No indicators of compromise (IoCs) are available currently.
Threat Landscape
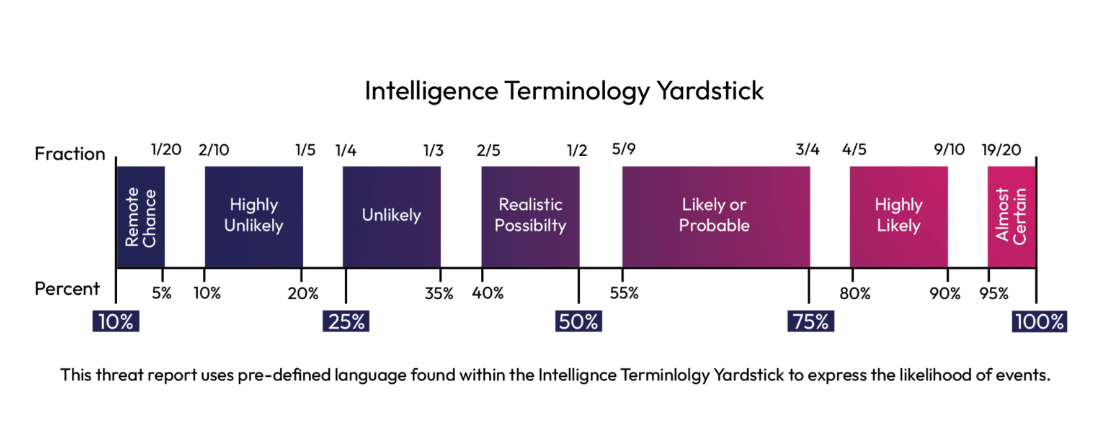
Citrix occupies a significant portion of the virtual application and desktop market share. The related products are used extensively by organisations across the industry sector spectrum. Within this context, it has been assessed that cyber threat actors will almost certainly view organisations with operational protocols involving these products as prime targets as they seek to meet their pre-defined objectives.
Intelligence indicates that vulnerabilities related to Citrix products for which patches exist have previously been subjected to malicious cyber operations. It is therefore of critical importance to follow the recommended remediation and mitigation strategies to reduce the risk of exploitation.
Threat Group
No attribution to specific threat actors or groups has been identified at the time of writing.
Mitre Methodologies
*Tactic:*
*Common Weakness Enumeration:*
- [CWE-119] – Improper Restriction of Operations within the Bounds of a Memory Buffer
- [CWE-601] – URL Redirection to Untrusted Site (‘Open Redirect’)
- [CWE-287] – Improper Authentication
- [CWE-276] – Incorrect Default Permissions
- [CWE-284] – Improper Access Control
- [CWE-269] – Improper Privilege Management
## Further Information
Intelligence Terminology Yardstick