Target Industry
Indiscriminate, opportunistic targeting.
Overview
Researchers at SonicWall have identified a zero-day vulnerability in Apache OFBiz, designated as CVE-2024-38856. This critical flaw, with a CVSS score of 9.8, enables threat actors to execute remote code without prior authentication. The issue originates from a defect in the override view functionality, which can be exploited via specially crafted requests, allowing unauthorised attackers to achieve remote code execution (RCE).
Impact
Successful exploitation of CVE-2024-38856 enables unauthorised users to execute remote code.
Vulnerability Detection
Apache has released a security update addressing the security flaw in the respective product versions. As such, previous versions are vulnerable to potential exploits.
Affected Products
This issue affects Apache OFBiz through 18.12.14.
Containment, Mitigations & Remediations
It is highly recommended that all organisations run the relevant patches as soon as possible. The patch can be found at the vendor advisory page.
Indicators of Compromise
No indicators of compromise (IoCs) are available currently.
Threat Landscape
Apache OFBiz occupies a significant proportion of the enterprise application integration market share. Given that threat actors generally utilise a combination of probability and asset value to determine which attack surfaces to focus on, Apache products have become a prime target for threat actors. Due to the fact that enterprise applications are an integral aspect of business operations, threat actors will continue to exploit vulnerabilities contained within the associated products in an attempt to extract the sensitive data contained therein.
Threat Group
No attribution to specific threat actors or groups has been identified at the time of writing.
Mitre Methodologies
Tactic:
– TA0002 – Execution
Common Weakness Enumeration:
– CWE-863 – Incorrect Authorization
Further Information
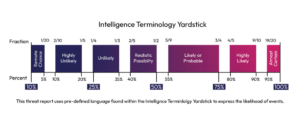
Intelligence Terminology Yardstick