Target Industry
Indiscriminate, opportunistic targeting.
Overview
Adobe has disclosed details relating to these vulnerabilities for Adobe Premiere Pro, Adobe InDesign, and Adobe Bridge:
- [CVE-2024-34123] (CVSSv3 score 7.0): Adobe Premiere Pro arbitrary code execution vulnerability.
- [CVE-2024-20781] (CVSSv3 score 7.8): Adobe InDesign arbitrary code execution vulnerability.
- [CVE-2024-20782] (CVSSv3 score 7.8): Adobe InDesign arbitrary code execution vulnerability.
- [CVE-2024-20783] (CVSSv3 score 7.8): Adobe InDesign arbitrary code execution vulnerability.
- [CVE-2024-20785] (CVSSv3 score 7.8): Adobe InDesign arbitrary code execution vulnerability.
- [CVE-2024-34139] (CVSSv3 score 7.8): Adobe Bridge arbitrary code execution vulnerability.
- [CVE-2024-34140] (CVSSv3 score 5.5): Adobe Bridge memory leak vulnerability.
Impact
Successful exploitation of CVE-2024-34123, CVE-2024-20781, CVE-2024-20782, CVE-2024-20783, CVE-2024-20785, and CVE-2024-34139 could enable threat actors to gain arbitrary code execution in relation to the affected Adobe product versions.
Successful exploitation of CVE-2024-34140 could enable threat actors to gain arbitrary file system read capabilities in relation to the affected Adobe product versions.
Vulnerability Detection
Adobe has released patches pertaining to the security flaw for the respective product versions. As such, previous versions are vulnerable to the potential exploits.
Affected Products
The Adobe products that are affected by these vulnerabilities are:
Adobe Premiere Pro
- 24.4.1 and earlier versions for Windows and macOS.
- 23.6.5 and earlier versions for Windows and macOS.
Adobe InDesign
- ID19.3 and earlier version for Windows and macOS.
- ID18.5.2 and earlier version for Windows and macOS.
Adobe Bridge
- 13.0.7 and earlier versions for Windows and macOS.
- 14.1 and earlier versions for Windows and macOS.
Containment, Mitigations & Remediations
It is highly recommended that all organisations apply the relevant patches as soon as possible.
More information can be found on the Adobe help page.
Indicators of Compromise
No indicators of compromise (IoCs) are available currently.
Threat Landscape
Adobe occupies a significant portion of the application-development market share. Threat actors generally utilise a combination of probability and asset value to determine which attack surfaces to focus on. As a result, application-development products can emerge as a prime target. Due to the fact that Adobe products have become an integral aspect of personal and business operations, threat actors will continue to exploit the associated vulnerabilities in an attempt to exfiltrate sensitive data contained therein or impact associated business operations.
Threat Group
No attribution to specific threat actors or groups has been identified at the time of writing.
Mitre Methodologies
*Tactic:*
- [TA0002] – Execution
*Common Weakness Enumeration:*
- [CWE-426] – Untrusted Search Path
- [CWE-122] – Heap-based Buffer Overflow
- [CWE-787] – Out-of-bounds Write
- [CWE-190] – Integer Overflow or Wraparound
- [CWE-125] – Out-of-bounds Read
Further Information
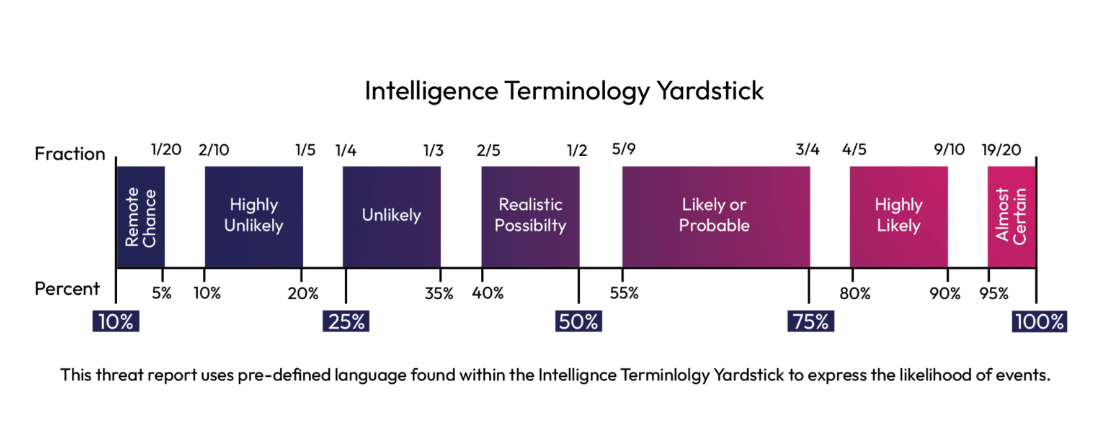
Intelligence Terminology Yardstick